HSE Fined €645,000 After Old Medical Records Found Rotting and Mould-Covered in Abandoned Storage
The Data Protection Commission has fined the Health Service Executive €645,000 after thousands of old medical records were discovered rotting, mouldy, and covered in animal droppings in an abandoned storage facility — a serious breach of data protection obligations that the Commission has described as a significant failure in the HSE's duty to protect the sensitive personal information of patients.
Background
The protection of medical records is one of the most fundamental obligations of any healthcare system. Medical records contain some of the most sensitive personal information that exists — details of diagnoses, treatments, medications, mental health history, and other intimate aspects of a person's life. The General Data Protection Regulation (GDPR), which came into force in 2018, imposes strict obligations on organisations that process personal data, including requirements to store data securely, to retain it only for as long as necessary, and to dispose of it safely when it is no longer needed.
The HSE, as Ireland's national health service, processes the medical records of millions of patients and is subject to the full range of GDPR obligations. The organisation has faced a number of data protection challenges in recent years, including the catastrophic ransomware attack of 2021 that disrupted health services across the country and exposed significant vulnerabilities in the HSE's IT infrastructure. The discovery of improperly stored physical medical records represents a different but equally serious category of data protection failure.
The Data Protection Commission is Ireland's national data protection authority, responsible for enforcing GDPR and other data protection legislation. It has the power to impose fines of up to €20 million or 4 per cent of global annual turnover for serious breaches of data protection law, and has been increasingly active in exercising this power in recent years.
Key Developments
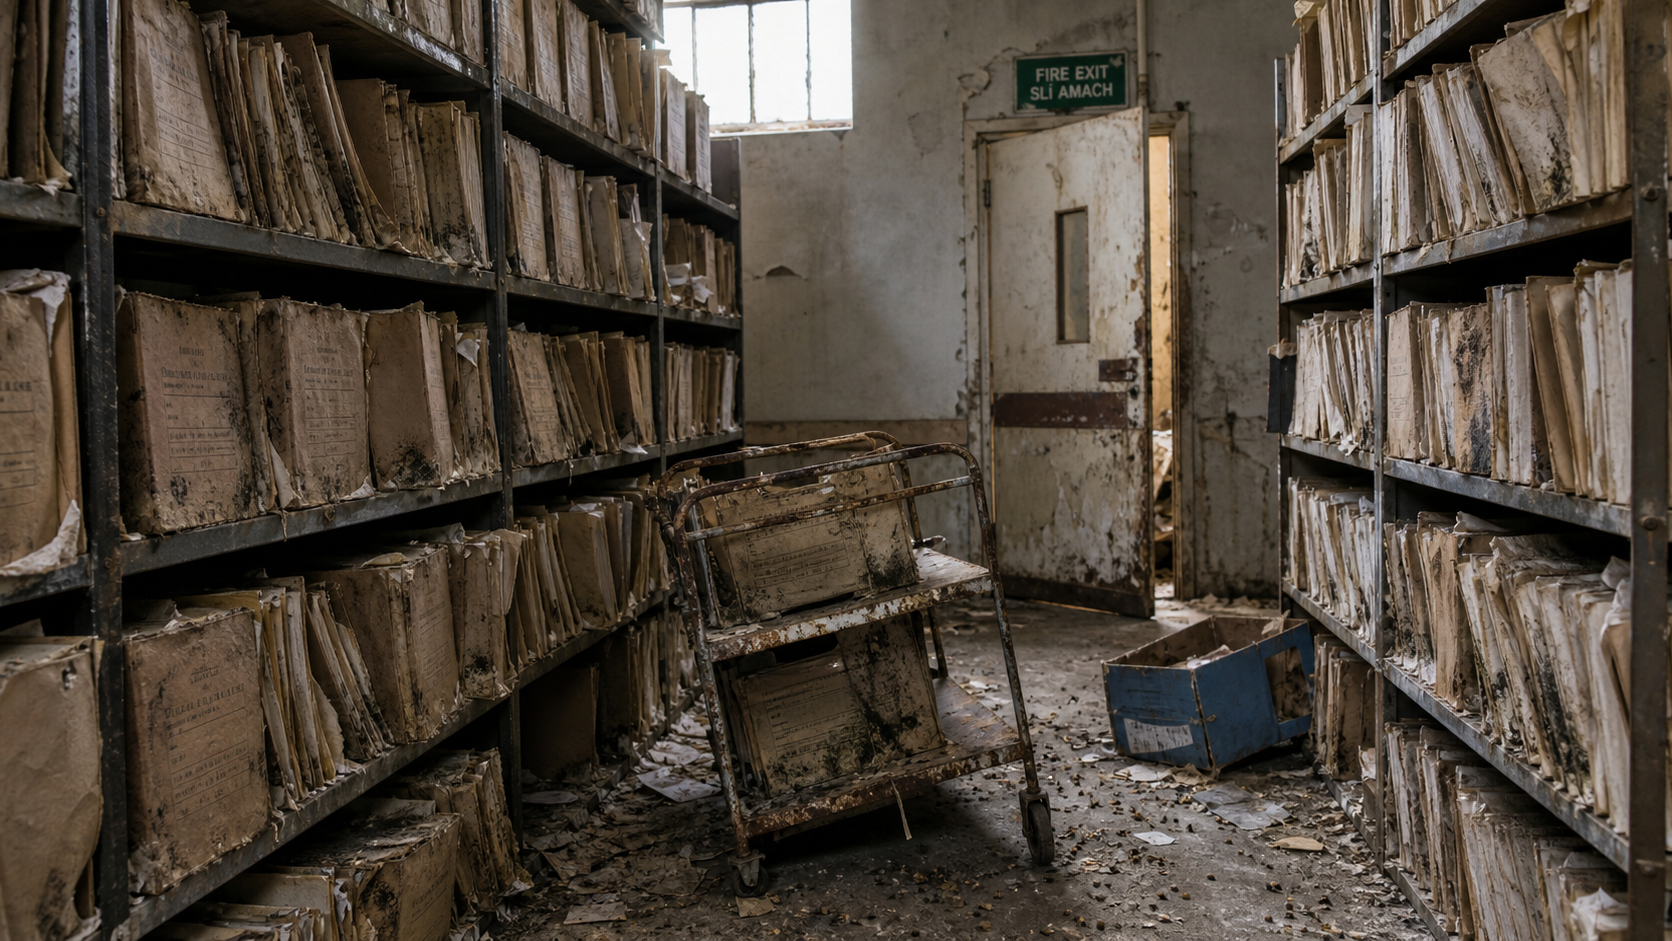
The DPC's investigation found that thousands of old medical records had been stored in a facility that was subsequently abandoned, leaving the records exposed to the elements and to animal infestation. The records were discovered in a state of significant deterioration, with mould, rot, and animal droppings rendering many of them illegible. The records contained highly sensitive personal and medical information relating to patients who had been treated by the HSE over a period of many years.
The DPC found that the HSE had failed to implement appropriate technical and organisational measures to ensure the security of the personal data contained in the records, and had failed to ensure that the records were disposed of safely when they were no longer required for their original purpose. The Commission imposed a fine of €645,000, which it described as proportionate to the seriousness of the breach and the number of individuals affected.
The HSE has accepted the fine and has indicated it is taking steps to address the data protection failures identified by the DPC. The organisation has committed to a comprehensive review of its records management practices, including the identification and secure disposal of any other legacy records that may be stored in inappropriate conditions.
Why It Matters
The HSE fine is a reminder that data protection failures can take many forms, and that the risks associated with physical records are just as serious as those associated with digital data. In an era when cybersecurity dominates the data protection conversation, it is easy to overlook the risks posed by improperly managed physical records — but for the patients whose medical histories were left to rot in an abandoned facility, the breach is no less serious than a cyberattack.
The case also raises questions about the HSE's records management practices more broadly. The discovery of thousands of records in an abandoned facility suggests a systemic failure in the organisation's approach to records retention and disposal, rather than an isolated incident. The DPC's investigation will have examined the processes and procedures that allowed this situation to develop, and the findings are likely to have implications for the HSE's records management practices across the organisation.
For patients, the case is a reminder that their medical records — some of the most sensitive information about them — may not always be protected with the care and diligence that they have a right to expect. The GDPR gives individuals the right to know how their personal data is being processed and to seek redress if it is mishandled, and the DPC's enforcement action demonstrates that these rights are taken seriously.
Local Impact
The DPC's fine will be paid from HSE funds, which ultimately come from the public purse. The €645,000 penalty represents a significant sum for an organisation that is already under severe financial pressure, and will reduce the resources available for patient care. The HSE has indicated that it will fund the fine from its existing budget rather than seeking additional resources from the Department of Health. The records management review that the HSE has committed to undertaking will require additional resources and staff time, adding to the organisation's administrative burden. Patient advocacy groups have called for the HSE to provide information to patients who may have been affected by the breach, and to explain what steps are being taken to prevent similar incidents in the future.
What's Next
The HSE is expected to publish a report on its records management review within six months, setting out the steps it is taking to address the failures identified by the DPC. The DPC will monitor the HSE's compliance with its undertakings and may conduct a follow-up investigation if it has concerns about the organisation's progress. The case is likely to be cited in ongoing discussions about the adequacy of data protection practices in the Irish public sector, and may prompt the Department of Health to issue updated guidance on records management to all HSE-funded organisations.